Protecting Data in Transit
- 2 ways:
- Encrypt the data
- encrypt the specific file
- Encrypt the entire connection with a transport encryption protocol
- encrypt with a VPN connection
- using TLS encryption
- protections generally apply to only a single application or protocol
Encrypting the Connection
- To ensure the data is secure, the endpoints of the communication must be authenticated
- data must be encrypted before transmission and decrypted upon arrival at the destination
- also verified that it was not modified
- data transmitted to and from a database over a secure connection is typically secured using:
Encryption at the Client
- Before data is transmitted to the server, it must be encrypted at the client
- When using TLS,
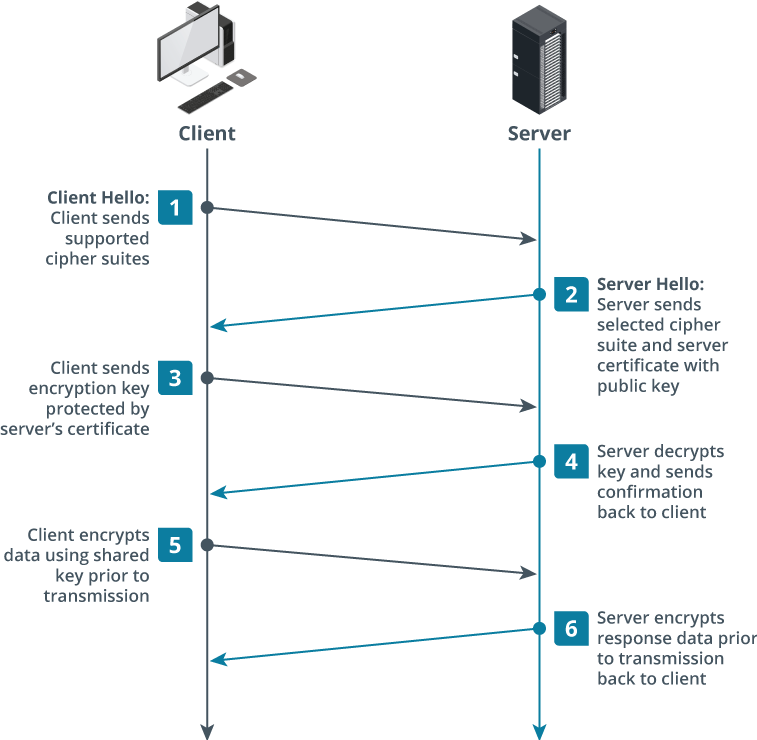
- the initial communication between a client and a server is called the TLS handshake
- client sends an initial transmission to the server containing the cipher suites it supports, along with some additional information
- server responds with the cipher suite it wants to use and a certificate containing the public key of the database server
- client verifies the certificate, either by indicating trust in the certificate or having the certificate in its certificate store
- Once verified, the client creates a master key, encrypts it using the public key from the certificate, and sends it back to the server
- This master key will be used to encrypt the data
- server then responds with its acknowledgment
- Now the client can encrypt the data it wants to transmit using the master key that was sent to the server
Encryption in Transit
- After the data is encrypted at the client, the client will transmit the encrypted data to the server
- The data is protected during transmission due to the encryption using the shared master key
- Once the data arrives at the server, the shared master key will be used to decrypt the data
Encryption at the Server
- When transferring data from the server back to the client,
- the master key shared by the client during the TLS handshake is used to encrypt the data prior to transmission
- This shared session key will also be used to decrypt the data once it has arrived at the client side